Cybersecurity · Active vigilance

Cybersecurity that never sleeps for networks that cannot go down

Network, firewall and endpoint management with Fortinet and Sophos technology. Continuous traffic inspection, automatic blocking of what policies classify as a threat and organized audit evidence, with 24x7 monitoring within the contracted scope.

net_defense_console Demo
perimeter stable inspection active
8,947 Blocks today
0 Active incidents
fgt-edge-01
firewall
vpn-corp-01
124 tunnels
sd-wan-sp
12ms
14:31 intrusion attempt · blocked
14:29 remote access denied · review
14:24 suspicious sample under analysis
100% traffic inspected 3ms avg block
[ The Challenge ]

Without visibility, the threat is already inside

Most security incidents start with avoidable gaps: uninspected traffic, uncontrolled remote access, a flat network with no segmentation. By the time the attack is noticed, it has already spread.

Accerte operates the Fortinet and Sophos platforms under dedicated management: it inspects traffic across the managed perimeter, automatically blocks what policies classify as a threat and centralizes the evidence that supports LGPD, PCI-DSS and ISO 27001 audits.

  • 24/7network and firewall management
  • DPIon managed perimeter traffic
  • 17 yearsprotecting critical networks
Security console · FortiGate-01 Demo
8,947 Blocks · 24h
0 Active incidents
124 VPN Tunnels
FortiGate-01 · active policies
now
IPS · 0 intrusions detected
1min
SD-WAN · latency 12ms avg
4min
URL Filter · 347 sites blocked
8min
block-event.log blocked
# IPS · 12:47:03
source=187.45.92.10
country=RU
action=deny
rule="block-malicious-cc"
detected 247
blocked 247
100% contained
[ Our Approach ]

Three layers of defense

Visibility, blocking and containment working together, with automated response for what is already classified and 24x7 engineering for the rest.

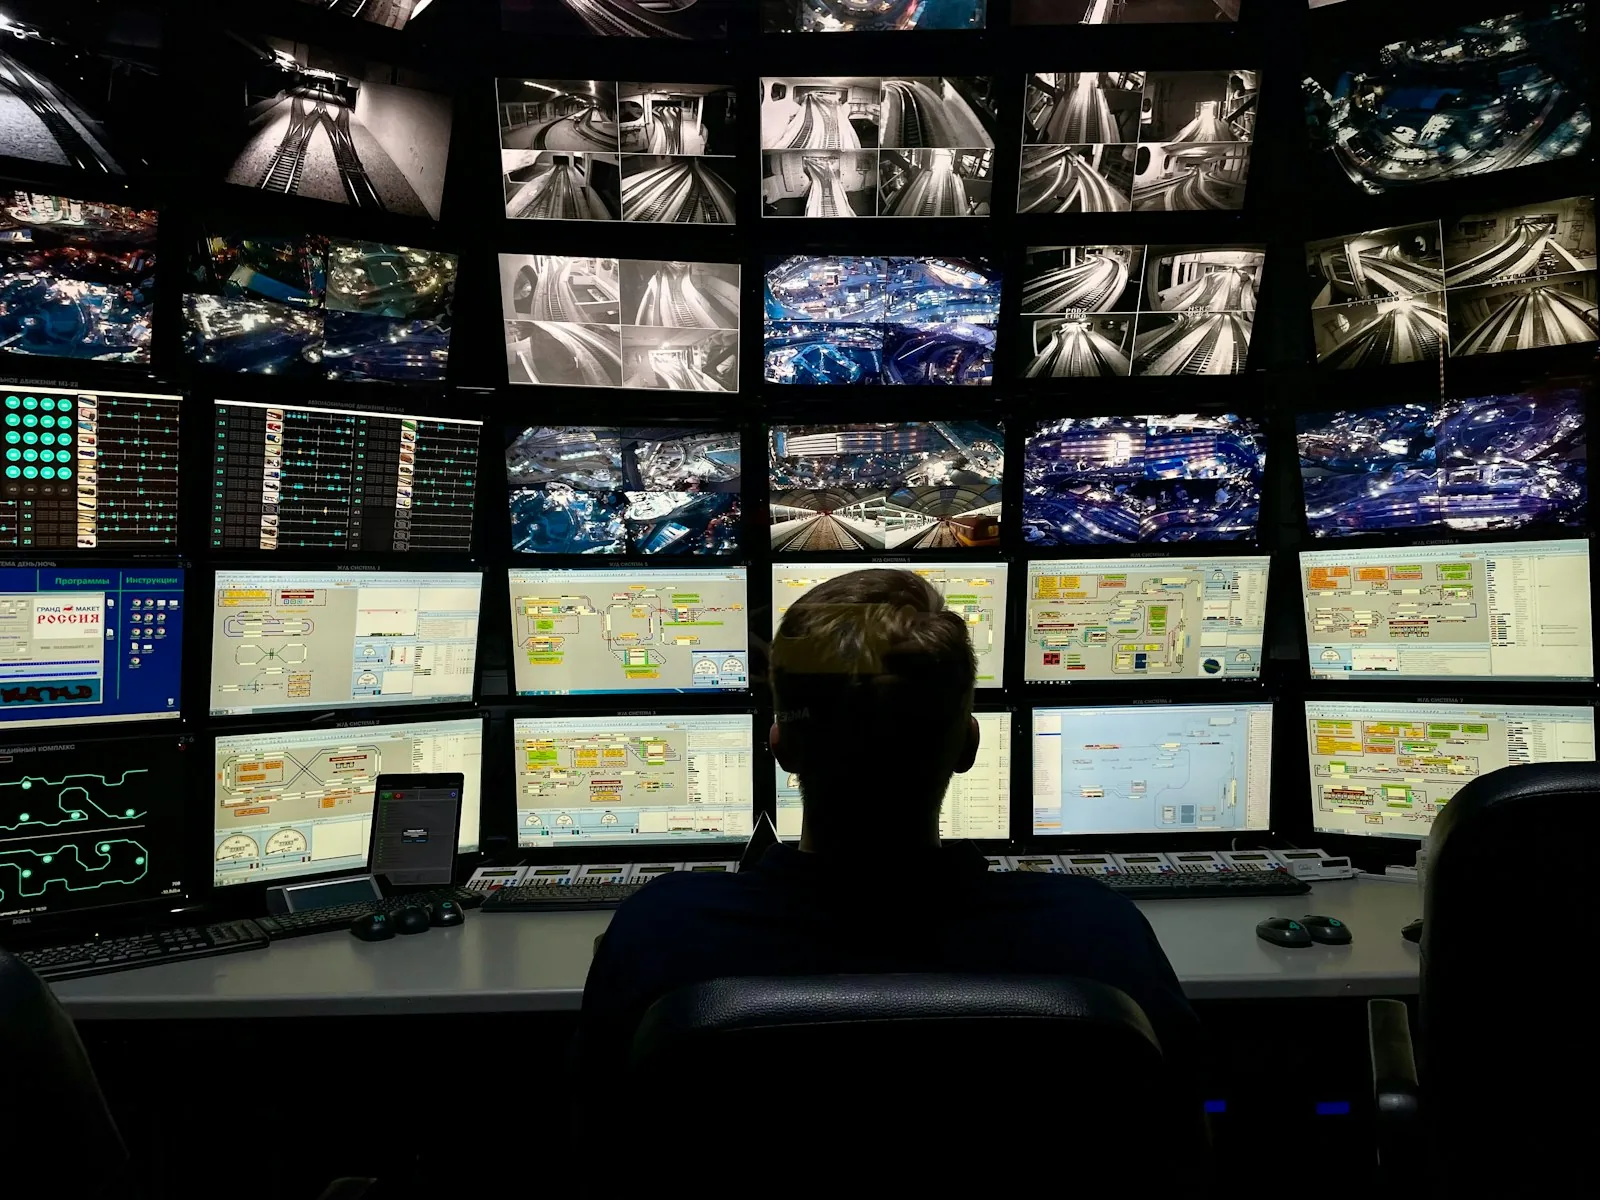
Accerte security analyst monitoring threats across consoles
01 · Inspection

We inspect the traffic, we classify every detection

Deep packet inspection on managed perimeter traffic, under the contracted policies, with behavioral analysis and continuously updated intelligence. Every detection is classified by severity, so critical threats are handled before they reach the internal network.

  • FortiGate NGFW with DPI on managed traffic
  • IPS with behavioral analysis and updated signatures
  • Centralized visibility in FortiAnalyzer
02 · Blocking

From detection to automatic blocking

Firewall policies applied automatically on every event. We do not depend on human approval to contain what is already classified as malicious.

  • Dynamic rules that update with Fortinet intelligence
  • Lateral containment through micro-segmentation
  • Automated response with documented playbooks
policy.conf Demo
# FortiGate · sample policy
config firewall policy
  edit 47
    set name "block-malicious-cc"
    set srcintf "wan1"
    set dstaddr "servers"
    set action deny
    set ips-sensor "Accerte-IPS"
  next
end
detected 247
blocked 247
100% contained
Zero Trust Segmentation Demo
Internet · untrusted
FORTIGATE fw-edge-01 NGFW + IPS + URL
DMZ
Internal
Cloud
Continuous identity verification Logs centralized in FortiAnalyzer
03 · Segmentation

Zero Trust on every access and zone

Every person, device and network zone is verified before gaining access to critical resources. If an incident happens, segmentation limits lateral movement.

  • Micro-segmentation by VLAN and application
  • Multi-factor authentication and device posture
  • Auditable access trail for LGPD and ISO 27001
Assess your network

Want an X-ray of your network security posture?

In a quick conversation, we map exposures, policy gaps and what changes in practice when Accerte's managed security starts operating your perimeter.

Schedule an assessment
Accerte network engineers monitoring firewall and traffic
[ Behind the operation ]

Dedicated network engineering, not a ticket queue

Not a generic ticket queue. A team of Fortinet-certified engineers on call 24x7, with their own playbook, context on your environment and a response SLA for critical incidents.

  • Response within SLA 24x7 critical incident handling, within the contracted service-level timeframe.
  • Fortinet certifications NSE 4, NSE 5, NSE 7. Operated by people who know the stack inside out.
  • Context on your environment Same analysts, same policies. Response driven by knowledge, not a script.
[ Results ]

What changes with Accerte

More stable connectivity, continuous monitoring and organized evidence for compliance audits, according to the contracted scope and service levels.

  • Deep inspection of managed traffic with Fortinet or Sophos NGFW and IPS
  • Zero Trust on every access, with identity verified continuously
  • Micro-segmentation that isolates zones and limits lateral movement
  • Automated reports that support LGPD, PCI-DSS and ISO 27001 audits
  • Dedicated engineering on call 24x7, with an SLA for critical incidents
  • FortiAnalyzer centralizing logs with forensic traceability

Want to see this operation protecting your network?

Talk to a specialist
[ Technologies ]

Partners and technologies

We operate the Fortinet and Sophos portfolios (firewall, endpoint, XDR, ZTNA, email and MDR) and officially integrate IBM identity and access solutions.

Ready to start?

Protection that never sleeps starts with an assessment

In a quick conversation, we analyze your risk surface, current stack and gaps. Get an assessment showing where you can reduce exposure and strengthen your defense.

Response within 1 business day · Your data is handled under our Privacy Policy